Readiness and evidence
Security audit approaching and evidence missing? What to prioritize before the deadline
When an audit is close, distinguish missing proof from partial controls and real gaps so your team can focus on what matters most.
When an audit is approaching and evidence is missing, not every open item is equally urgent. The key is to distinguish between controls that exist but cannot be demonstrated, partially implemented controls and genuine gaps. That makes it possible to prioritize issues that could affect the assessment and decide what must be addressed before the deadline.
With only a few weeks left before a security audit, a common mistake is trying to produce dozens of documents at once. It is better to organize the outstanding requirements first, identify what evidence exists, what is missing and which issues could most seriously affect the audit.
At Talsoft, we start by putting the pending requirements into a simple matrix: each requirement, its current status, available evidence, missing evidence, criticality, owner and estimated time to resolve. Then we prioritize according to which absence could have the greatest effect on the audit.
Missing evidence does not always mean the same thing
Before deciding what to fix, distinguish between three situations: the control exists but its evidence cannot be found, the control is only partially implemented, or the control has never been implemented.
These situations require different responses.
If MFA is enabled but its coverage has not been demonstrated, reports and configuration records may provide the missing proof.
If backups exist but restoration has never been tested, a restore test may need to be run and documented.
If periodic access reviews never took place during the audited period, however, the gap must be disclosed. The process can be implemented and documented from that point forward, but a new record should not be presented as proof of historical reviews.
This distinction separates what can still be corrected and evidenced before the deadline from what should be reported as a gap with a remediation plan.
What to prioritize before the audit deadline
Once pending requirements are organized, the next step is to set priorities. In general, we address critical controls that do not exist or cannot be demonstrated first. Then we work on operational evidence, documentation and, finally, improvements that belong in a later roadmap.
Which evidence deserves attention first depends on the audit framework and scope. Common areas include:
- MFA and privileged access
- User onboarding and offboarding
- Vulnerabilities and remediation
- Backups and restoration tests
- Logs, monitoring and incident response
- Current policies
- Security awareness and phishing exercises
- Critical suppliers
- Architecture diagrams
- Records of periodic reviews
The goal is to identify which of these requirements are in scope and which need attention before the deadline. For broader preparation, see our guide to preparing for a security audit.
Use an Audit Readiness Sprint
When only a few weeks remain, Talsoft follows an Audit Readiness Sprint approach:
- Take a rapid inventory of requirements and available evidence.
- Mark issues by criticality.
- Assign an owner to each item.
- Centralize documentation in one repository.
- Hold short follow-up meetings to move pending work forward.
The aim is to see clearly what evidence exists, what is missing, who is responsible and which issues must be handled before the audit. This focuses the team on the requirements that matter without trying to solve everything at once.
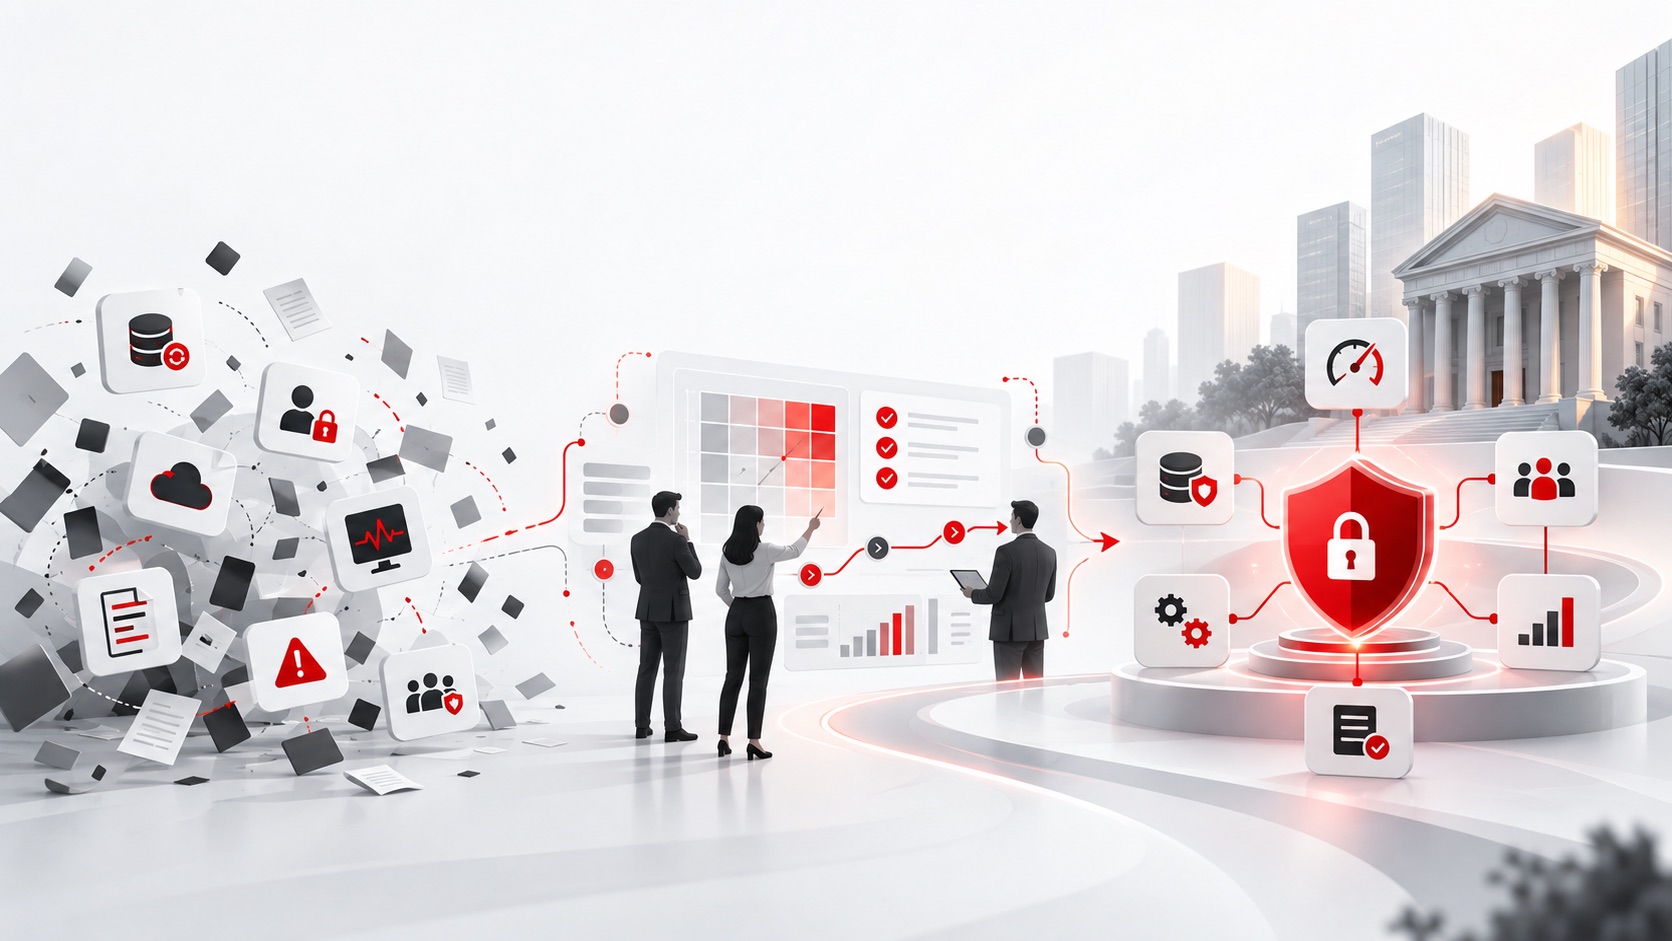 Turn scattered audit tasks into organized controls, owners and evidence.
After the audit, keep evidence organized
The work should not end with the audit. Evidence should remain organized, with owners and review schedules, so the organization does not start from scratch when another audit, security questionnaire or request arrives.
That is also the purpose of Talsoft's cybersecurity maturity program: helping organizations turn scattered controls, owners and evidence into a more organized, prioritized and sustainable security program. A case study from an Australian financial company shows how this work can progress over six months.
If your company has an upcoming audit, needs to organize its evidence or wants a more mature approach to cybersecurity, contact us to discuss how Talsoft can help.
Talsoft
Prioritize your audit work before the deadline
Let's review which controls and evidence are ready, what is missing and what to address first.