Case studies
How an Australian financial company turned scattered controls into a structured cybersecurity program
Over approximately six months, Talsoft supported an Australian financial company from assessment to a more operational ISMS with prioritized controls, owners and evidence.
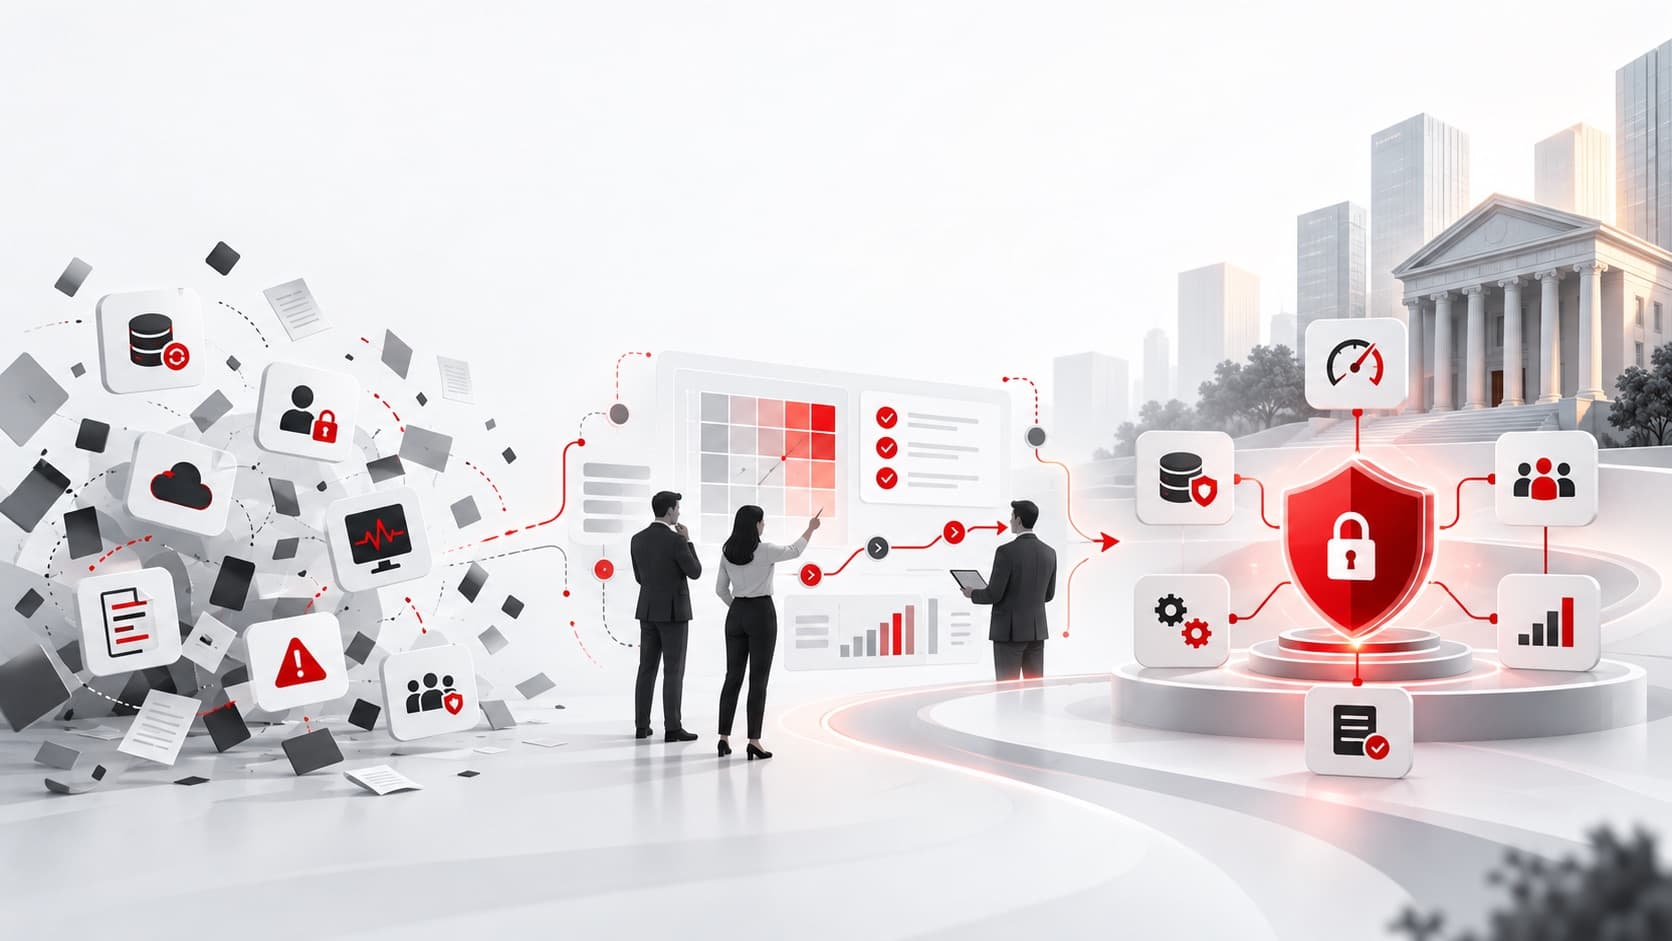
Over approximately six months, Talsoft supported an Australian financial company from assessment through implementation of a more operational information security management system (ISMS), with prioritized controls, owners, processes and evidence.
Many companies are not starting from zero in cybersecurity. They already have backups, access controls, monitoring tools, policies and other measures implemented by their teams. The difficulty arises when these controls operate separately and basic questions become hard to answer: What are the most important risks? What is actually implemented? What needs improvement? How can the organization demonstrate that its controls work?
The client's challenge
The company needed to strengthen its ISMS and move toward alignment with ISO/IEC 27001 while considering regulatory requirements and good practices relevant to its operations in Australia.
Without an integrated system, prioritizing risks, maintaining evidence and sustaining controls consistently were difficult. The organization also depended heavily on the operational knowledge held by individual team members.
Rather than simply adding tools or isolated controls, the challenge was to understand the company's actual position, identify its main gaps and establish a clear order for improvement.
Talsoft's approach
The engagement began with an assessment of cybersecurity maturity and existing controls. That created a baseline before deciding what to implement.
Based on this diagnosis, the team reviewed risks, controls and evidence and defined an improvement roadmap. Instead of addressing every open item at once, initiatives were prioritized according to risk and business impact.
The project did not end with a gap report. For approximately six months, Talsoft worked alongside the company to implement the program.
The work covered risk management, ISMS policies and procedures, business continuity and recovery, incident response and third-party management. Technical controls involving infrastructure, vulnerabilities, AWS, backups and monitoring were also strengthened.
An important goal was to avoid permanent dependence on an external provider. Talsoft helped establish processes, records, owners and evidence that the internal team could continue to manage.
Results
By the end of implementation, the company had a clearer view of its risks and priorities, more structured continuity and incident response processes, and a greater ability to demonstrate that its controls worked. Dependence on informal practices had also decreased, and the internal team was better positioned to maintain much of the security program.
Across the assessed controls, consolidated metrics showed approximate overall compliance rising from 27% to 70%. Controls marked "non-compliant" fell from approximately 44% to 17%, while compliance among high-risk controls rose from around 26.7% to 83.3%. These are results from this engagement, not a guarantee of similar outcomes elsewhere.
As the client put it, Talsoft's work was thorough and professional, and the team learned a great deal throughout the project. Talsoft integrated well with the team from day one and worked effectively across time zones.
Talsoft helps companies understand their current position, define a roadmap and turn scattered initiatives into a structured, sustainable cybersecurity program. Contact us to discuss how we can support your organization.
Talsoft
Turn scattered controls into a sustainable program
Let's review your current position, priorities and how to build a roadmap with clear owners and evidence.