Readiness and evidence
How to respond to a security questionnaire
How to organize owners, controls and evidence to answer a security questionnaire consistently.
A security questionnaire lets customers, banks, insurers and partners assess a company's security posture. Responding consistently requires understanding the context of the review, assigning owners, validating implemented controls and gathering evidence to support each answer.
Security questionnaires are increasingly part of the evaluation process that customers, partners and other organizations carry out before signing a contract or approving a supplier. A company may have to answer dozens of questions about MFA, backups, access, infrastructure, cloud, vulnerabilities, secure development, incident response, suppliers and data protection, often under tight deadlines and with specific evidence requirements.
The most common mistake is treating the document as a form that merely needs to be filled out. Before answering, it is worth understanding what the other party is evaluating, the scope of the review, which internal teams need to participate and which controls can be demonstrated objectively. It is equally important to identify partial implementations, missing evidence and gaps that still need remediation.
At Talsoft, we treat the questionnaire as part of a process for validating an organization's security posture. The priority is to keep what the company says consistent with the controls it actually operates and the evidence it can provide.
Understand the context before answering
The first step is to understand why the questionnaire arrived. A review from a prospective enterprise customer is not necessarily the same as one from a bank, insurer or technology partner: each may be evaluating different risks.
Before preparing responses, identify who is requesting the information, the deadline and the service your company provides to that third party. You also need to understand the systems involved, the data processed, the suppliers that participate and the scope of the evaluation. This context helps you interpret each question.
Review the full questionnaire and group the questions
Once the context is clear, review the entire security questionnaire. Answering questions one by one without examining the full document first can lead to duplicated work, inconsistent answers and uncoordinated requests to internal teams.
At Talsoft, we organize questions by security domain: governance and policies, access management, MFA, infrastructure and cloud, backups and continuity, vulnerability management, secure development, incident response, data protection, suppliers and training.
This turns a long list of isolated questions into a map of the topics being assessed. It also shows which teams will need to participate and what documentation or evidence must be gathered.
Assign an owner to each group of responses
One person can rarely answer a cybersecurity questionnaire accurately on their own. Controls are usually distributed across different teams, each of which knows part of the organization's reality.
Some questions belong to IT or DevOps; others require input from Development, Human Resources, Legal, Compliance or leadership. Once the questionnaire has been classified, identify who can validate each domain or control.
Here, Talsoft acts as a technical and security coordinator, centralizing the review so it does not turn into a disorderly chain of emails, messages and documents. Coordination also helps uncover contradictions and maintain consistent criteria across the answers.
Validate controls before declaring them
Broadly speaking, each control falls into one of three situations: it exists and has sufficient evidence; it is partially implemented or lacks documentation; or there is a gap.
For example, a company may say that it performs backups. But if the questionnaire asks when the last restoration test took place, confirming that copies exist is no longer enough. The organization also needs to demonstrate that it can recover the information.
The same applies to MFA, access reviews, vulnerabilities and incident response. Evidence supports each answer in the questionnaire.
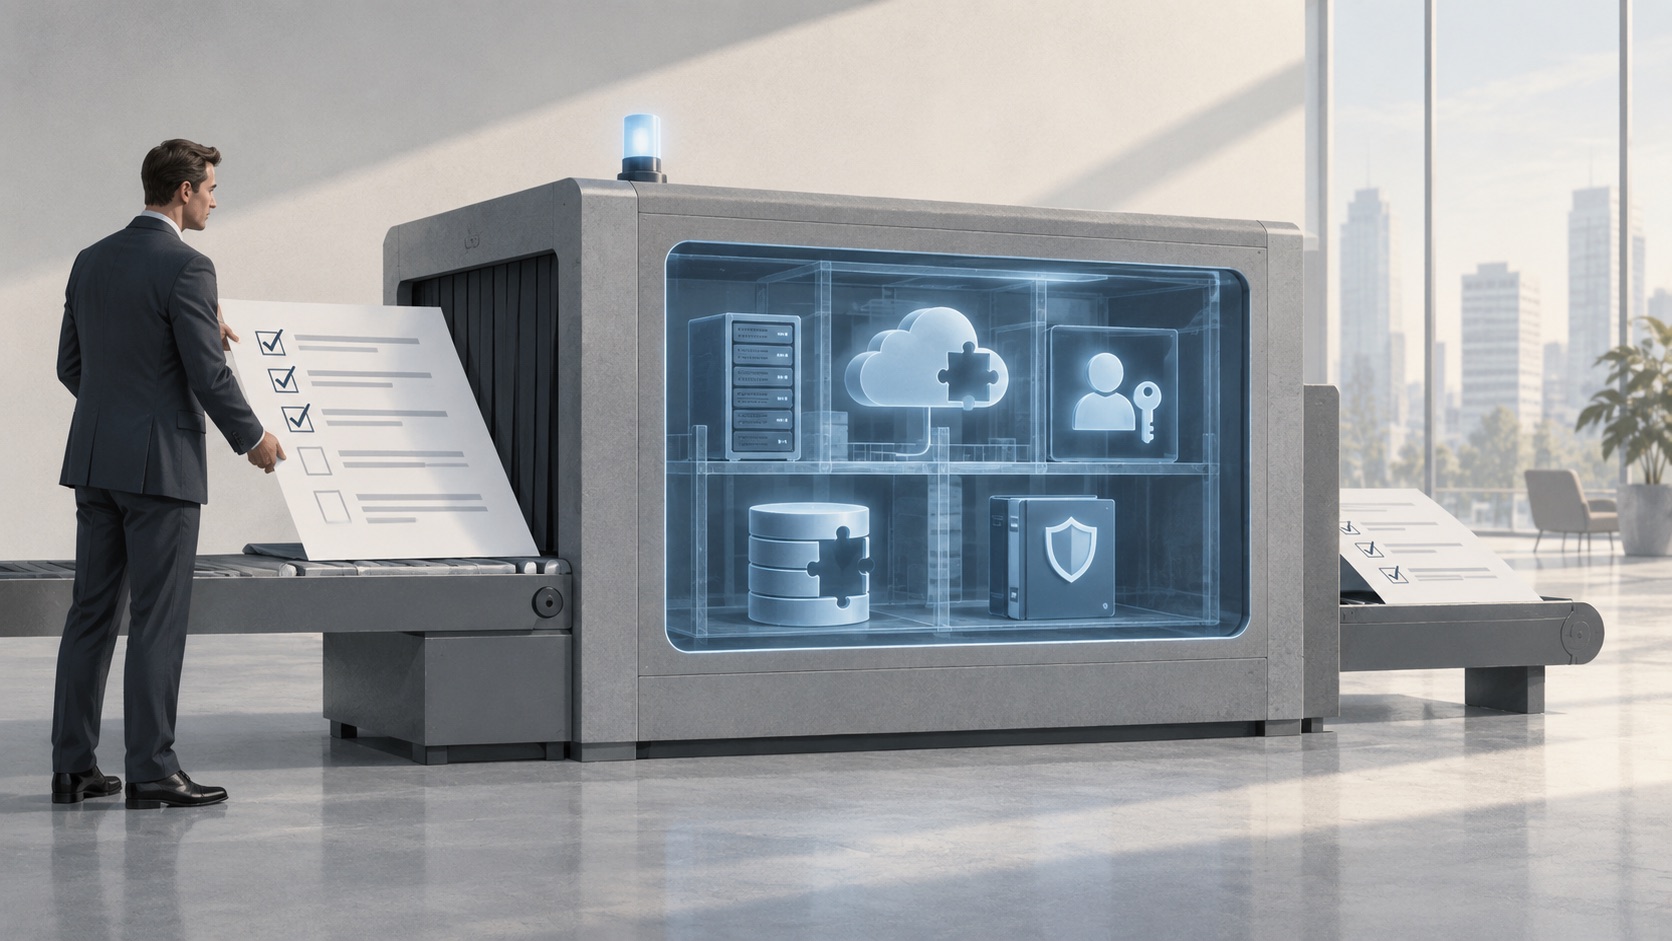 Before responding, distinguish demonstrable controls, partial implementations and gaps.
What evidence can accompany the answers?
The evidence depends on each question and the depth of the evaluation. It may include configuration screenshots, reports, tickets, logs, policies and procedures, access reviews, restoration tests, vulnerability reports, penetration test results or training records.
Not every questionnaire requires evidence for every answer, but a company should know what it can provide if the customer decides to investigate further. An enterprise customer evidence guide can help organize that inventory.
Often, a control exists but no one has formalized how to demonstrate it. Backups may be configured correctly, for example, without records of recovery tests. The improvement then may be to formalize the process, assign an owner and retain recurring evidence. We also explain what evidence customers and auditors may request.
What if the questionnaire reveals a gap?
The review may uncover controls that are not yet resolved. A policy may be missing, an implementation may be partial or a practice may never have been documented. When a gap exists, it is better to identify it, describe the current state accurately and, when appropriate, accompany it with a remediation plan.
Finding pending controls does not mean everything must be fixed immediately. A security questionnaire may reveal many opportunities for improvement, but they do not all carry the same risk, urgency or commercial impact.
Some gaps may affect operations or the protection of sensitive information; others may be creating friction in closing a contract. After identifying the gaps, prioritize them and turn them into a remediation plan or, when appropriate, a roadmap with owners and deadlines.
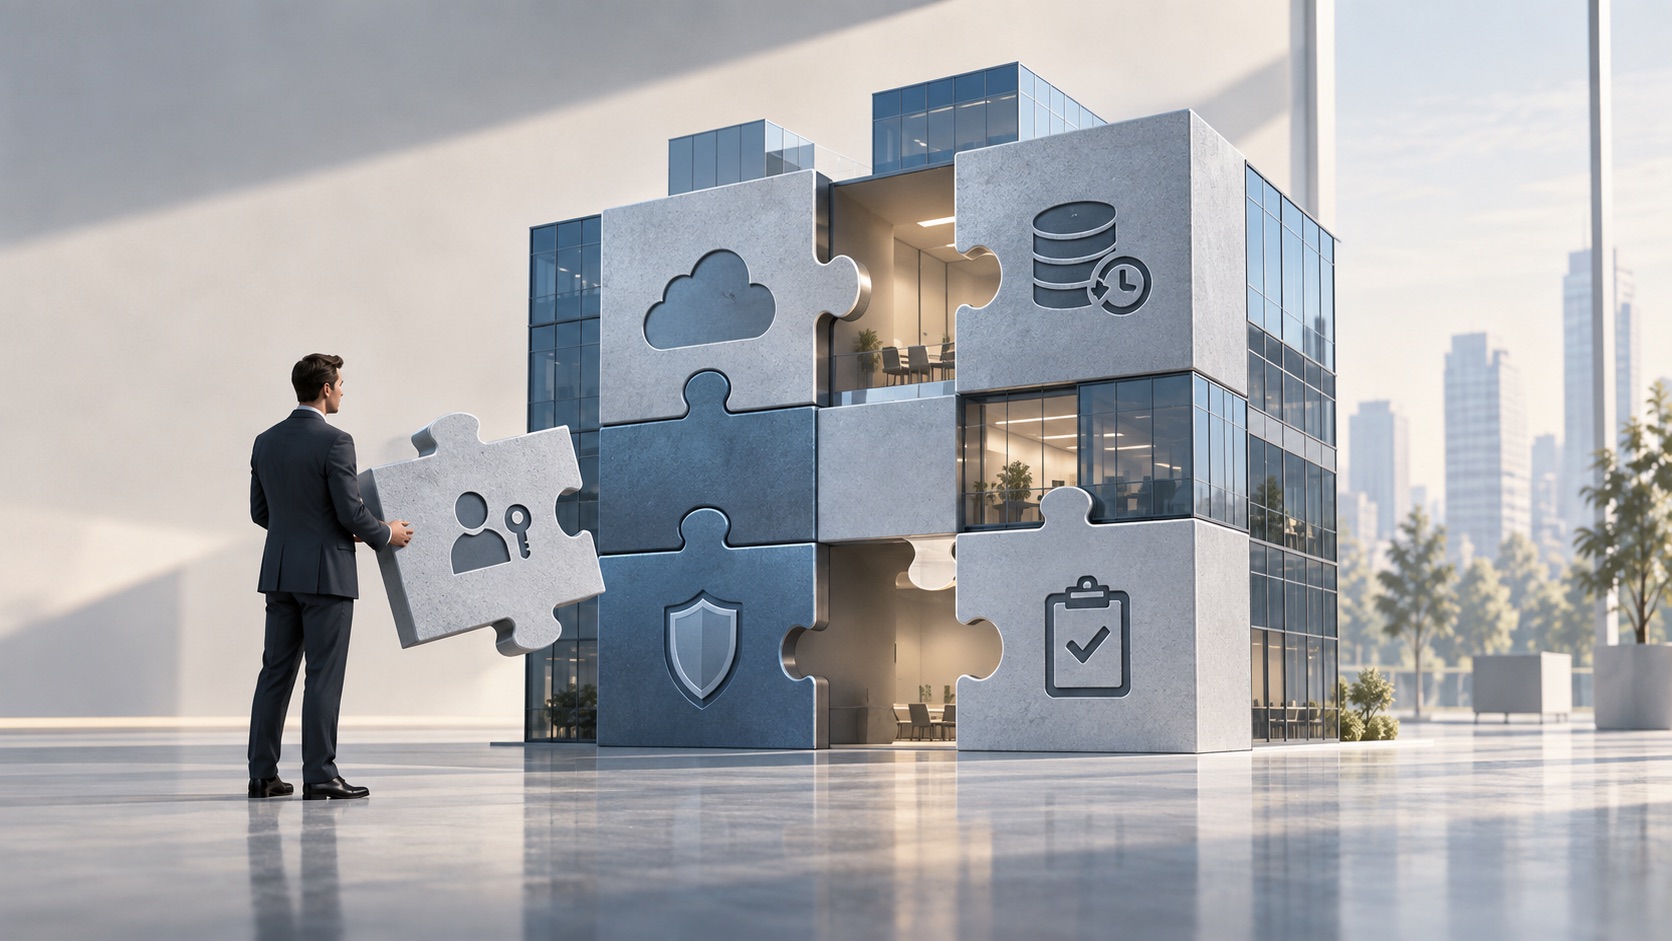 Identified gaps can become a prioritized roadmap with owners and deadlines.
Check consistency before submitting
When several people contribute, contradictory answers or different interpretations of related controls can appear. Before submitting the questionnaire, conduct an overall review, confirm that the evidence supports every claim and ensure the company can stand behind each answer if the customer asks for more detail.
This final review can expose differences between documented procedures and what actually happens. It also prevents responses prepared by separate teams from presenting an inconsistent view of the organization's security.
From a security questionnaire to a more mature program
Talsoft helps companies manage the security questionnaires they receive from customers, partners and other third parties. But the work often reveals needs that go beyond the immediate questionnaire.
A company may have many controls in place yet struggle to demonstrate how they work, assign owners or maintain evidence over time. These are the gaps we address through our cybersecurity maturity programs, turning them into a prioritized improvement roadmap with clearly defined controls, owners, risks and evidence.
If your company has received a security questionnaire and needs to organize its answers, validate evidence or address the gaps it reveals, get in touch.
Talsoft
Answer the questionnaire with evidence, not assumptions
Let's review the scope, which answers you can support and which gaps need priority.