Case studies
From 20% toward 80% ISO 27001 control compliance: a SaaS case study
Talsoft assessed a SaaS company's controls: the initial review found approximately 20% compliance and informed a plan aimed at approaching 80%.
After an initial assessment found approximately 20% compliance with the controls evaluated against ISO 27001, Talsoft helped a SaaS company define an improvement plan aimed at reaching a level close to 80%.
As a technology company grows, its infrastructure evolves. New systems, monitoring tools, services and development environments bring new requirements for security controls and ongoing oversight.
Many companies already have protective measures in place but lack an integrated view of their risks or a plan for deciding what to improve first. This need can become more urgent after a security incident, when reviewing existing controls and deciding how to move forward are especially important.
The client's challenge
A company that develops and sells SaaS software for the accounting sector needed to assess its technology infrastructure and understand its cybersecurity maturity level.
The need became more pressing in 2025, after the company experienced a security incident involving data theft. It needed an independent assessment to identify vulnerabilities, review its controls and establish a baseline for organizing improvements.
The challenge was also linked to the growth of its technology infrastructure. The company had added new monitoring tools and systems, making it necessary to revisit the risks associated with this changed environment and assess whether its existing security controls were sufficient.
The goal was to identify the main risks, determine which security areas needed improvement and define a work plan with clear priorities suited to the company's resources and needs.
Talsoft's approach
The engagement began with a penetration test to identify vulnerabilities in the systems within scope. Talsoft then carried out an initial cybersecurity maturity assessment (Initial GAP) over approximately two months.
The assessment used the Talsoft Maturity Framework, a methodology for examining a company's cybersecurity posture in a structured way. Through a review of controls, processes and evidence, the team identified the main security gaps and set improvement priorities based on business risk.
The assessment included a tailored review of infrastructure, monitoring tools and security controls. It also considered new virtual private servers (VPS) used for development and production, which expanded the company's technology footprint and the risks it needed to manage.
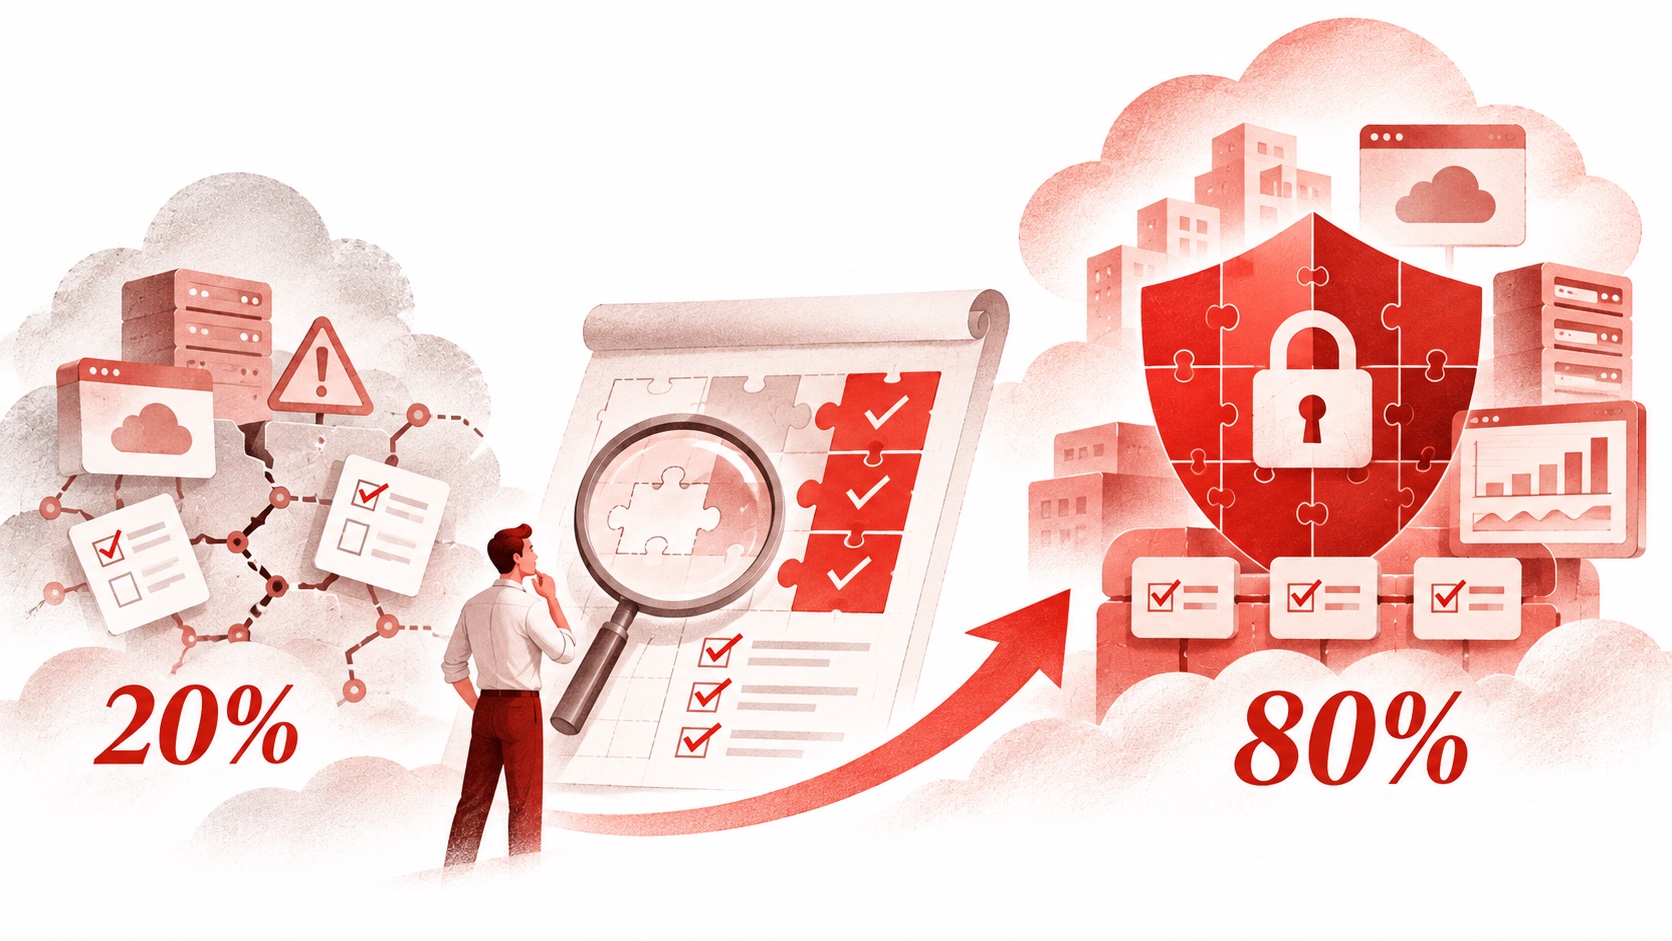 From a gap assessment to a progressive improvement plan
Results
The initial assessment found approximately 20% compliance with the controls evaluated against ISO 27001. Based on the proposed improvements, Talsoft estimated that the organization could approach 80% through progressive implementation of the defined plan. That 80% is a projection, not a measured outcome or an ISO 27001 certification.
In 2026, the company engaged Talsoft again to update its GAP assessment in light of infrastructure changes and the need to revisit priorities. This new phase also opened the possibility of periodic support, with reviews approximately every four months to track improvement projects and adapt actions as the organization evolves.
Asked about the service, the company's technology lead highlighted three qualities: “Speed, efficiency and results.”
Talsoft helps companies assess their cybersecurity maturity, identify gaps and turn assessment findings into prioritized, sustainable improvement plans.
Schedule a conversation to learn more about our services.
Talsoft
Turn an assessment into an improvement plan
Let's review your current controls, gaps and priorities, with clear owners and evidence for the work ahead.