Cybersecurity maturity
What an external CISO does and how to hire one
Having an IT team and security controls is not always enough to manage business risk. An external CISO helps set priorities and coordinate security decisions.
Having an IT team and security controls is not always enough to manage business risks. Bringing in external leadership can help set priorities, coordinate owners and make strategic cybersecurity decisions.
Having an IT team, tools and security controls does not necessarily mean there is a cybersecurity strategy. As a company grows, it also needs to decide who assesses risks, sets priorities and supports business decisions.
At Talsoft, we provide external cybersecurity leadership for organizations that need specialized guidance without hiring a full-time CISO. Our approach starts with understanding the business, identifying its main risks and setting priorities. From there, we work with internal teams to assign owners, coordinate initiatives and follow up on security decisions.
What an external CISO does
A CISO (Chief Information Security Officer) is responsible for directing and overseeing an organization's information security strategy. Beyond identifying threats or recommending technical controls, they must understand the business, assess the risks that could affect it and help decide how to manage them.
When this role is provided externally on a part-time basis, it is known as a Fractional CISO. In practice, the work may include reviewing risks, defining priorities, building a roadmap, coordinating internal teams and vendors, and following up on decisions agreed with leadership.
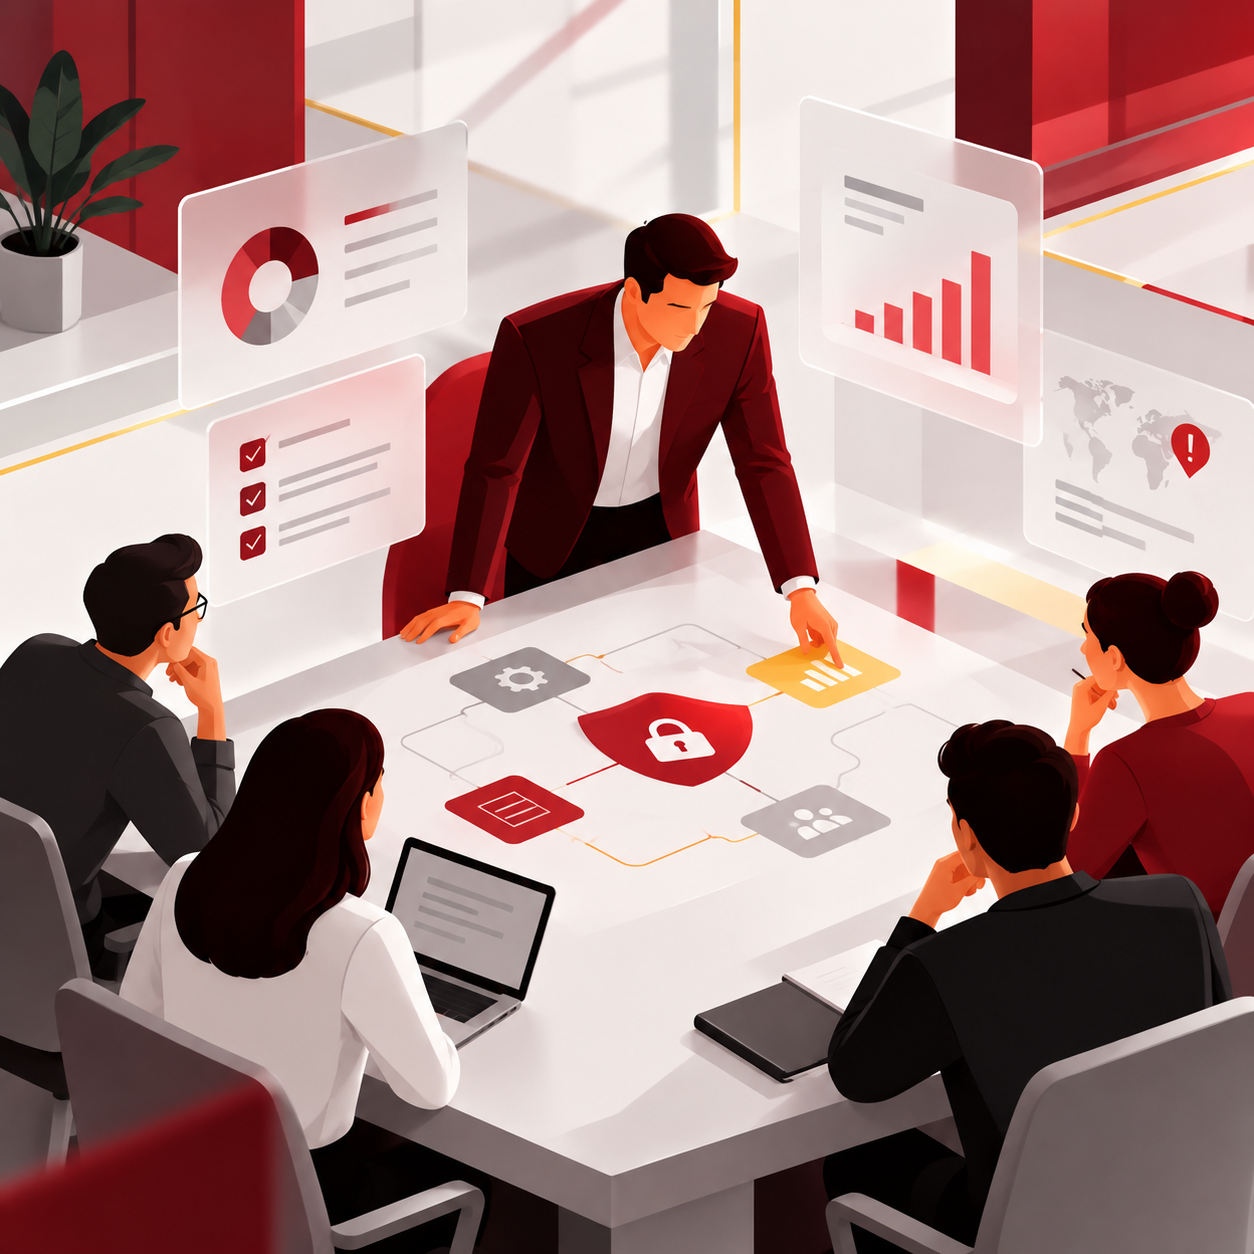 An external CISO connects risks, priorities and decisions with the company's teams.
A different role from IT
In many companies, cybersecurity responsibilities fall to the CTO, infrastructure lead or IT team. These professionals know the systems and can implement controls, manage access, handle backups and solve technical problems. But operational capability alone is not always enough to direct a security program.
For example, IT may identify outstanding vulnerabilities. Deciding which to fix first, what resources to allocate and what level of risk the business is willing to accept calls for a broader perspective.
An external leader brings that perspective and works alongside existing teams. They should not replace those teams, but help organize priorities and communicate risks to management.
What to evaluate before hiring
Technical experience matters, but it should not be the only criterion when selecting someone to lead your company's cybersecurity. It is also important to assess their ability to understand the business, communicate across departments and turn technical risks into decisions leadership can understand.
Ask about their working method:
- How do they identify risks?
- How do they set priorities?
- What deliverables do they produce?
- How do they coordinate with IT?
- How do they communicate progress and unresolved issues?
It is also important to define the scope of the engagement: time commitment, meeting frequency, responsibilities, reports, availability during incidents and activities that require a separate agreement.
When to hire an external CISO
The need for an external CISO can arise at different stages. Sometimes it is driven by investors, customers or partners asking how the company manages cybersecurity risks and meets specific requirements.
In other cases, the company has already implemented controls or developed a security program, but needs to keep it operating, review its risks and provide strategic direction.
Even with a CTO or IT team, their day-to-day responsibilities may not include governing the company's entire cybersecurity program.
In these situations, external leadership brings in someone who can assess the risks behind business decisions, set priorities and coordinate owners without hiring a full-time CISO.
Organizing the work and keeping decisions visible
Once the engagement begins, the challenge is to turn strategy into a recurring practice. That means reviewing the risk register, keeping the roadmap current and following up on projects and owners.
It also means revisiting what has changed since the last assessment. A company may have fixed important vulnerabilities while adding a new vendor, changing its infrastructure or launching a service that processes sensitive information.
Security leadership therefore needs to evolve with the business. At Talsoft, this work is organized through periodic reviews of risks, decisions, controls and owners, with progress tracking and coordination with internal teams.
Choosing the right support
When an organization needs executive judgment, coordination and follow-through on security decisions, an external leadership model can provide that function without building a full-time executive structure.
Does your company need strategic cybersecurity leadership without hiring a full-time CISO? Explore Talsoft's Fractional CISO service and how we can help manage your business's security risks and decisions.
Frequently asked questions about hiring an external CISO
How much does it cost to hire an external CISO?
The cost depends on company size, system complexity, the risks to manage and the time commitment required. As a reference, Talsoft publishes an indicative range of US$1,900 to US$4,900 per month for its Fractional CISO service. The final quote depends on scope and contract terms.
How many hours per month does an external CISO need to work?
There is no single number that works for every company. The required time depends on risk level, active projects, customer and audit requirements, and the internal team's capacity. The service may include regular meetings, priority tracking and executive support at an agreed frequency.
What results can a company expect in the first month?
In the first few weeks, the goal is to understand the organization and establish a basis for decisions. This may include identifying critical assets, reviewing existing risks and controls, assigning owners and creating an action plan. Talsoft's initial work includes setting priorities for the next 90 days.
What is the difference between an external CISO and a SOC or MSSP?
An external CISO directs cybersecurity strategy, assesses risks and coordinates business decisions. A SOC (Security Operations Center) primarily monitors threats and detects incidents, while an MSSP (Managed Security Service Provider) may operate security tools and controls. These functions complement one another: one sets direction and the others can perform operational work.
Does an external CISO also perform penetration tests?
Not necessarily. An external CISO may identify the need for penetration testing, define its scope and coordinate remediation of the findings. Performing a pentest, however, requires specialized technical professionals and may be contracted as a separate service.
Talsoft
Define the security leadership your company needs
Let's review your risks, responsibilities and the scope of external CISO support.